
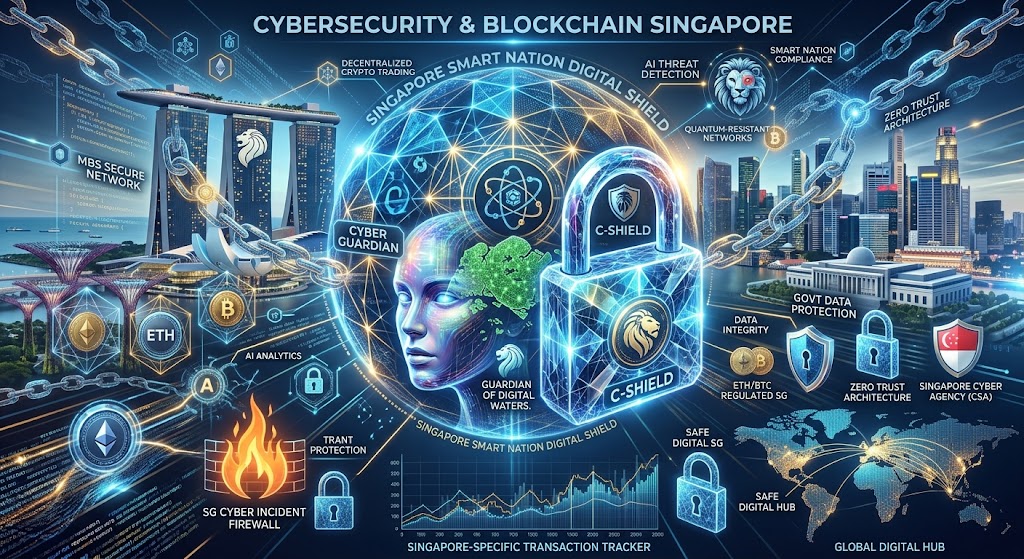
Announced at Singapore International Cyber Week on October 14, 2026, the new helpline aims to help businesses navigate cyber incidents, while CSA expands support for SMEs through cybersecurity clinics, workshops and certification initiatives.
Singapore has launched a Cyber Incident Helpline to help businesses respond to cybersecurity incidents, marking a new step in the country’s efforts to strengthen cyber resilience among enterprises, particularly small and medium-sized enterprises (SMEs).
Senior Minister of State for Digital Development and Information Tan Kiat How announced the initiative during his opening remarks at Singapore International Cyber Week (SICW) on October 14, 2026. The helpline will serve as an accessible first point of assistance for businesses affected by cyber incidents, helping them identify next steps and connect with additional support when necessary.
The initiative comes as Singapore accelerates digitalisation across its economy, with businesses increasingly adopting cloud computing, artificial intelligence (AI) and digital services to improve productivity and expand operations.
However, growing digital dependence is also exposing organisations to greater cybersecurity risks.
Nearly 90% of Organisations Report Cybersecurity Incidents
Tan cited findings from the Cyber Security Agency of Singapore’s (CSA) Cybersecurity Health Report 2025, which found that almost nine in 10 surveyed organisations had encountered at least one cybersecurity incident in 2025.
SMEs and non-profit organisations continue to face challenges in strengthening their defences, including limited budgets, a shortage of expertise and insufficient cybersecurity awareness.
AI is adding another dimension to the threat landscape. While the technology can help security teams detect and respond to threats more efficiently, it can also enable attackers to operate faster and at greater scale.
Increasingly interconnected business ecosystems also mean that an incident affecting one organisation could have consequences for its customers, suppliers and business partners.
Tan said Singapore’s approach is not to slow digitalisation or AI adoption, but to ensure businesses can embrace new technologies with safeguards that match their ambitions.
Cybersecurity Certification Becomes a Business Requirement
Singapore is also strengthening cybersecurity expectations for organisations handling critical systems and sensitive information.
According to Tan, CSA will require critical entities and cybersecurity service providers supporting essential services to meet Cyber Trust Mark requirements. GovTech will similarly require government vendors managing critical systems and sensitive government data to meet Cyber Essentials and/or Cyber Trust Mark requirements by the end of 2027.
These measures reflect the growing importance of cybersecurity assurance in commercial relationships and public-sector procurement.
Customers increasingly expect businesses to protect their information, while larger organisations are paying closer attention to the security of their supply chains. Government agencies also need confidence that vendors can adequately safeguard sensitive systems and data.
For businesses, recognised cybersecurity standards can therefore help demonstrate readiness, build customer trust and improve access to opportunities where stronger security assurance is required.
CSA Expands Practical Cybersecurity Support for SMEs
Alongside stronger security expectations, Singapore is expanding practical assistance to help businesses improve their cybersecurity posture.
The Cyber Resilience Centre (CRC), launched in 2025, provides resources and support to help companies address cybersecurity challenges. Its cybersecurity health clinics and workshops have benefited close to 500 companies, according to Tan.
The agency is also piloting a programme called Cyber Essentials in a Day, designed to help businesses strengthen their baseline cybersecurity protections more quickly.
Tan emphasised that improving security does not necessarily require sophisticated technology. Businesses should first focus on fundamental measures, including:
- Applying security patches and keeping systems updated.
- Protecting important accounts and implementing appropriate access controls.
- Backing up critical business data.
- Training employees to recognise cybersecurity threats.
- Establishing clear procedures for responding to incidents.
CSA is also working with ecosystem partners, including CISO-as-a-Service providers and certification bodies, to help organisations put cybersecurity best practices into action.
Healthcare Organisations Recognised for Early Adoption
The event also recognised healthcare organisations that were among the first in Singapore to obtain Cyber Essentials certification.
The recipients will receive the Pioneer Adopter Award for going beyond cybersecurity requirements under the Health Information Act.
The recognition is intended to encourage organisations to strengthen their cybersecurity practices proactively rather than waiting for regulatory pressure or a security incident to trigger action.
Tan highlighted Alles Autos Credit Pte Ltd as an example of a business that took preventive measures after cyberattacks affected others in its industry and exposed sensitive customer information.
The company, represented by Managing Director Johnson Lim, worked with CISO-as-a-Service provider Contfinity Pte Ltd to address cybersecurity gaps and pursue certification.
It subsequently became the first company in Singapore’s licensed moneylending industry to attain the Cyber Essentials mark.
New Helpline Targets the Critical First Hours of a Cyber Incident
While preventive measures remain essential, Singapore acknowledges that no security strategy can eliminate every cyber risk.
For smaller businesses, responding to an incident can be particularly challenging during the first few hours, when decisions about containment, investigation and customer communication can significantly affect the outcome.
The newly launched Cyber Incident Helpline is intended to help businesses move from uncertainty to action by providing initial guidance and connecting them with further assistance where necessary.
The service addresses a common problem for SMEs: knowing whom to contact and what steps to take when a cyber incident occurs.
By making initial assistance more accessible, the initiative aims to help businesses respond more effectively, minimise operational disruption and manage the impact of security incidents.
Singapore Calls for a Collective Approach to Cyber Resilience
Tan stressed that cybersecurity requires cooperation between government agencies, businesses, security providers, certification bodies and industry associations.
The government will continue to establish security baselines, provide resources and develop capabilities, while industry partners can help organisations implement standards and access specialist expertise.
Businesses, meanwhile, must take responsibility for understanding their risks, implementing appropriate safeguards and preparing incident response plans before an attack occurs.
Singapore’s latest initiatives reflect a broader shift towards making cybersecurity an integral part of business operations rather than a technical concern addressed only after a breach.
With the Cyber Incident Helpline, expanded SME support and stronger certification requirements, the country is seeking to help enterprises strengthen their defences while continuing to pursue digital growth.
The central message from SICW 2026 is clear: cyber resilience is not just about preventing attacks. It is about helping businesses maintain trust, recover from disruption and continue operating in an increasingly digital economy.
Image Generated by AI. For Illustration Purpose Only.



Leave a Reply